Insights from practitioners and leaders on the challenges SOCs face today and how AI is being used to solve them

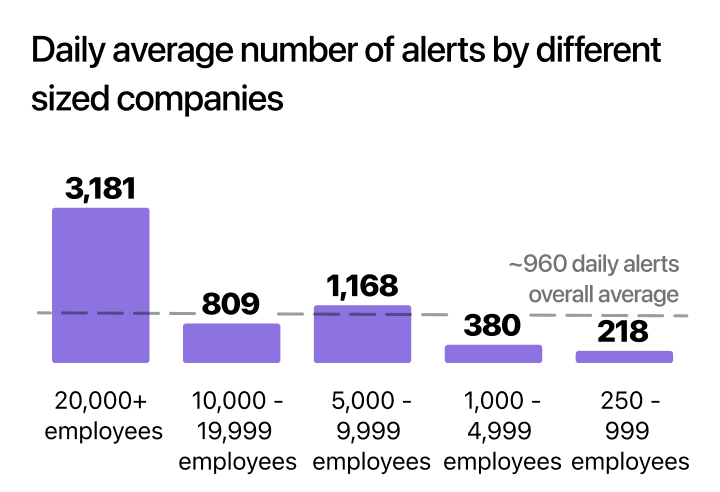
Companies of all sizes are experiencing a barrage of alerts. Smaller enterprises and middle-market companies generate ~500 alerts per day causing a substantial management burden while larger companies are facing a tsunami of data from the ~3,000 alerts per day.
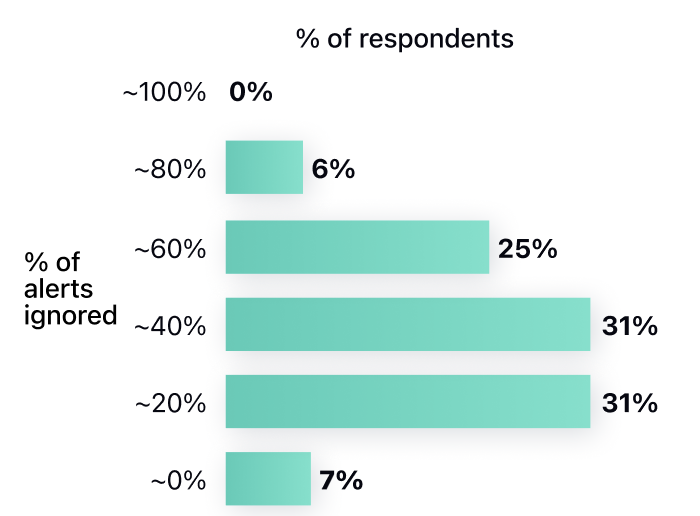
A concerning 40% of alerts (on average) are never investigated, leaving organizations vulnerable to significant, avoidable security risks. Roughly 60% of security teams have reported that an ignored alert proved to be critical, leading to a direct impact on the organization's security posture.
Get the 2025 report packed with hard data on alert dwell times, investigation speed, top AI use cases, and where SOC teams really stand on adopting AI.
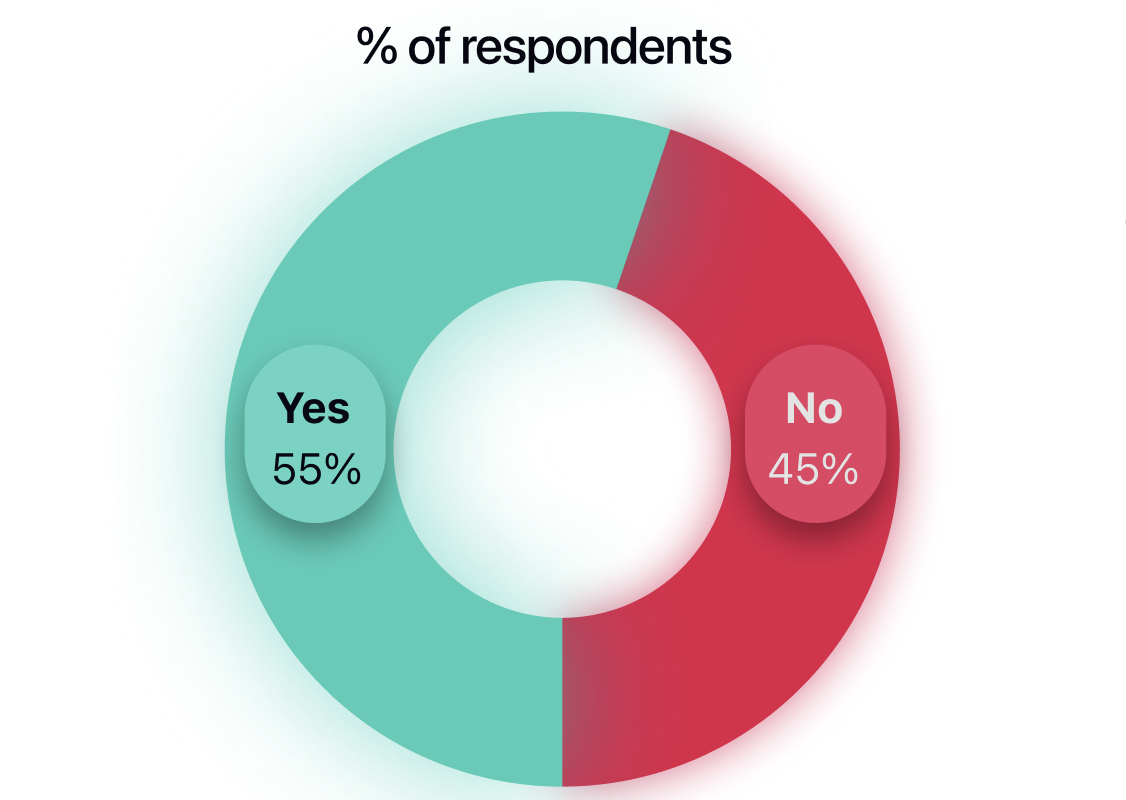
Most companies use AI in some capacity for triage and investigation, with more starting to use AI-native pure-play solutions. Of the AI non-users, nearly 60% plan to evaluate an AI SOC solution within the next year, and another 30% are evaluating AI SOC solutions. This strong intention to adopt AI signals a clear mandate for the security industry.
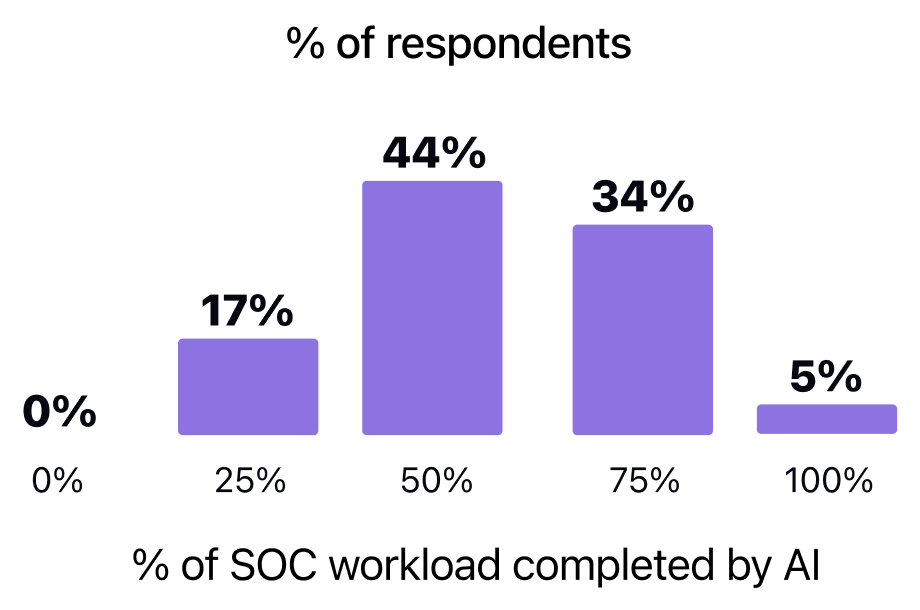
Security leaders anticipate AI solutions will handle approximately 60% of SOC workloads within the next 3 years, fundamentally reshaping security operations. It implies a dramatic reduction in manual effort, allowing human analysts to focus on more complex, strategic tasks while AI handles routine, high-volume operations.

Mean time to contain (MTTC) measures how fast your SOC stops an attack from spreading. How it differs from MTTR, how to measure it, and what AI changes.