

What Is an AI SOC? How AI Agents Work in Security Operations

Nearly every team in Prophet Security's State of AI in the SOC 2026 survey runs or is evaluating AI, yet "AI SOC" still describes products that do very different amounts of the work. Of the 250 security leaders and practitioners surveyed, 40% run AI in their SOC today and another 56% are evaluating or piloting it. Some tools summarize an alert for an analyst to finish, while others plan and run the investigation themselves.
Which kind a team runs affects how much of its alert queue gets investigated at all. In the same survey, a thorough investigation averages about 75 minutes. The average organization leaves roughly 28% of its alerts uninvestigated, and 60% of respondents said an alert they ignored or never investigated later proved material to the business.
The core work of a SOC is deciding which signals are real and acting on them in time. That means investigating alerts, hunting for activity that detections miss, keeping detections accurate, and containing what proves malicious, all of which depend on analyst judgment. When a team models its capacity, the alert queue usually takes the hours that hunting and detection work need.
What an AI SOC Is
An AI SOC is a security operations center in which AI agents investigate alerts, hunt for threats, and help build and tune detections, while people set direction, review the agents' work, and decide which actions the agents may take on their own. The term also covers the AI SOC platforms that supply those agents. They come from AI-native vendors, from SIEM, XDR and SOAR vendors that build agents into their suites, and through managed service providers that use AI. Vendors also call it an AI security operations center, an agentic SOC, an AI-powered SOC or an AI-driven SOC.
Products that only triage alerts represent the first generation of AI SOC. The category has since moved into threat hunting, detection engineering and response, which is why the definition above describes the operating model rather than any single product.
An AI SOC agent works an alert the way an analyst would. It decides what to ask and queries the tools that hold the evidence, such as the SIEM, EDR, identity provider, cloud audit logs and email security. It pivots on what it finds and records a determination, ideally with the queries and evidence behind it.
This differs from playbook-driven SOC automation. A typical SOAR playbook follows logic written in advance, such as blocking an IP address that a reputation feed flags. An agent works from context: the IP address may be clean while the PowerShell activity behind the alert is unusual for that user compared with the last 90 days, so the investigation continues.
Beyond the accuracy of the agents themselves, three things bound what an AI SOC can do. Agents can only investigate with the data sources connected to them, so evidence that sits only in an unconnected tool stays out of the investigation unless someone supplies it. They also need context about the organization, such as which assets are critical and which activity is expected.
Agents also act only within the permissions the team grants, and most teams grant them conservatively. In the same survey, no respondent gave AI full unsupervised autonomy, and 44% let it recommend actions that a person then carries out. An evaluation should test how a platform handles these limits, along with data handling and explainability.
An AI SOC also overlaps with terms buyers already use. An agentic SOC is the operating model in which agents work across the SOC's stages and hand work to one another. An AI SOC platform is what supplies those agents. An autonomous SOC raises a further question: how much of the work runs with no person involved.
An MDR provider works a customer's alerts with its own analysts, sometimes alongside AI agents of its own, while an AI SOC platform gives the in-house team that investigation capacity directly. Some organizations run both, with the AI SOC investigating what the MDR escalates and the alerts it does not cover.
What an AI SOC Does in Practice
In practice, AI SOC agents can take on six kinds of work across the SOC:
- Alert investigation. Alerts routed to the agents, including the low-severity ones a stretched team might skim or close in bulk, get a planned investigation and a documented determination. This is the work of an AI SOC analyst.
- Threat hunting. Agents search the connected telemetry for signs that a newly disclosed vulnerability has been exploited or a new campaign has reached the environment, and they run hypothesis-driven hunts against gaps in detection coverage. Suspicious leads go back for a full investigation (see AI threat hunting).
- Detection engineering. Agents map coverage gaps and noisy detections, drawing on the rule set, threat research and what investigations and hunts reveal, and propose new and tuned detections. They backtest each one against the organization's own history before it reaches production, usually with a person's approval. This is the role of an AI detection engineer.
- Response with approval gates. The team decides which containment actions, such as isolating a host or revoking a session, run on their own under set conditions. For the rest, an agent recommends the action, and a person approves it for the agent to run or carries it out.
- Case work. Agents group related investigations into cases and write their findings into the case management and ticketing tools the team already runs.
- Reporting. Agents keep a record of what was investigated, what it turned out to be and how long it took, which gives the SOC metrics on that work without a manual tally.
People stay accountable for the decisions. Analysts review determinations, teach the agents what is normal for the organization and decide which actions agents may run on their own. They also take on incidents that need business context and spend more of their time on hunting and detection work. In the same survey, roughly two-thirds of leaders expect AI to change what SOC roles involve rather than make the team smaller.
{{ebook-cta}}
Benefits of an AI SOC
The benefits of an AI SOC are measured in how quickly the team reaches a decision and how much of the environment it can examine.
Analysts reach a decision sooner
Among survey respondents already running AI, 72% report that it has cut alert investigation time by at least a quarter, with an average reduction of about a third. Where containment was waiting on the investigation, it can start sooner, which shortens the time an attacker has to move between systems.
Low-severity alerts are investigated too
Teams that triage by severity often leave some alerts unread by design, and early signs of an intrusion can sit in a low-severity alert. When those alerts are routed to the agents, an intrusion that first appears in one of them can be caught at that stage rather than later in the attack.
Hunting and detection work gets done without competing with triage
Hours that went to the queue can go to hunting for activity that detections missed and to tuning or writing detections from what investigations found. In the survey, among teams hunting weekly or more, 49% say a hunt has surfaced malicious activity their detections missed. Among teams reporting the lowest hunting frequency, that figure is 8%.
The thousandth alert is held to the same standard as the first
Investigation quality depends less on how late in a shift an alert arrives or which analyst picks it up. Each alert is investigated to the same standard, so results can be compared across the queue and over time. Model output can still vary from one run to the next, so it is worth sampling determinations to confirm the standard holds.
Reviewers can check the agents' work
When an AI SOC records the questions it asked, the queries it ran and what each returned, a reviewer can rerun a query, follow the reasoning and catch a determination the agent got wrong. The same record serves auditors and post-incident reviews.
Final Thoughts
An AI SOC changes how much of its own environment a security team can examine. Alerts nobody investigates and hunts nobody runs leave exposure the organization carries without knowing its size. An AI SOC reduces risk by shrinking that exposure and by shortening the time to contain what it finds. A business case for AI in the SOC is strongest when it ties the spend to three things: alerts investigated, time to a decision, and hunting and detection work done.
Nothing in this description is unique to one vendor, and the same questions apply to Prophet Security. Prophet AI investigates the alerts it receives in full, with its queries and evidence visible. It hunts for emerging threats and for what detections miss, and builds and tunes detections from what those investigations and hunts find. The team decides which actions run on their own. To see it on your own alerts, request a demo.
An AI SOC is a security operations center in which AI agents investigate alerts, hunt for threats, and help build and tune detections, while people set direction, review the agents' work, and decide which actions the agents may take on their own. The term also covers the platforms that supply those agents. Products that only triage alerts represent the first generation; the category has since moved into hunting, detection engineering and response.
The terms overlap. An agentic SOC describes the operating model, in which AI agents work across the SOC's stages, from investigation to hunting to detection engineering, and hand work to one another. An AI SOC platform is what supplies those agents. A team can start with an AI SOC platform on one stage, such as alert investigation, and expand toward an agentic SOC as its confidence in the agents grows.
A typical SOAR playbook follows logic written in advance, which works well for defined, repeatable steps such as enrichment or a known containment action. An AI SOC plans each investigation from the alert's context, deciding what to query and pivoting on what it finds, so it can handle alerts no playbook anticipated. Many teams run both, with SOAR or the AI SOC carrying out the actions the team has approved.
It mainly shortens the investigation step. In Prophet Security's State of AI in the SOC 2026 survey, 72% of teams running AI cut alert investigation time by at least a quarter, with an average reduction of about a third. Improved mean time to respond was also the measure respondents most often used to judge an AI SOC analyst, cited by 61%.
It gives a team the investigation capacity its alert volume demands, which hiring alone rarely keeps pace with. Agents work the alerts routed to them that a team could not reach, including low-severity ones that would otherwise be skimmed. In Prophet Security's 2026 survey, the average organization left about 28% of its alerts uninvestigated. The hours analysts recover can go to hunting, detection engineering and incidents that need human judgment.
No. People set direction, review the agents' determinations, decide which actions run on their own, and handle incidents that need business context. What changes is how analysts spend their time: less on repetitive enrichment, more on hunting, detection engineering and complex investigations. In Prophet Security's 2026 survey, roughly two-thirds of leaders expected AI to change what SOC roles involve rather than make the team smaller.
Insights
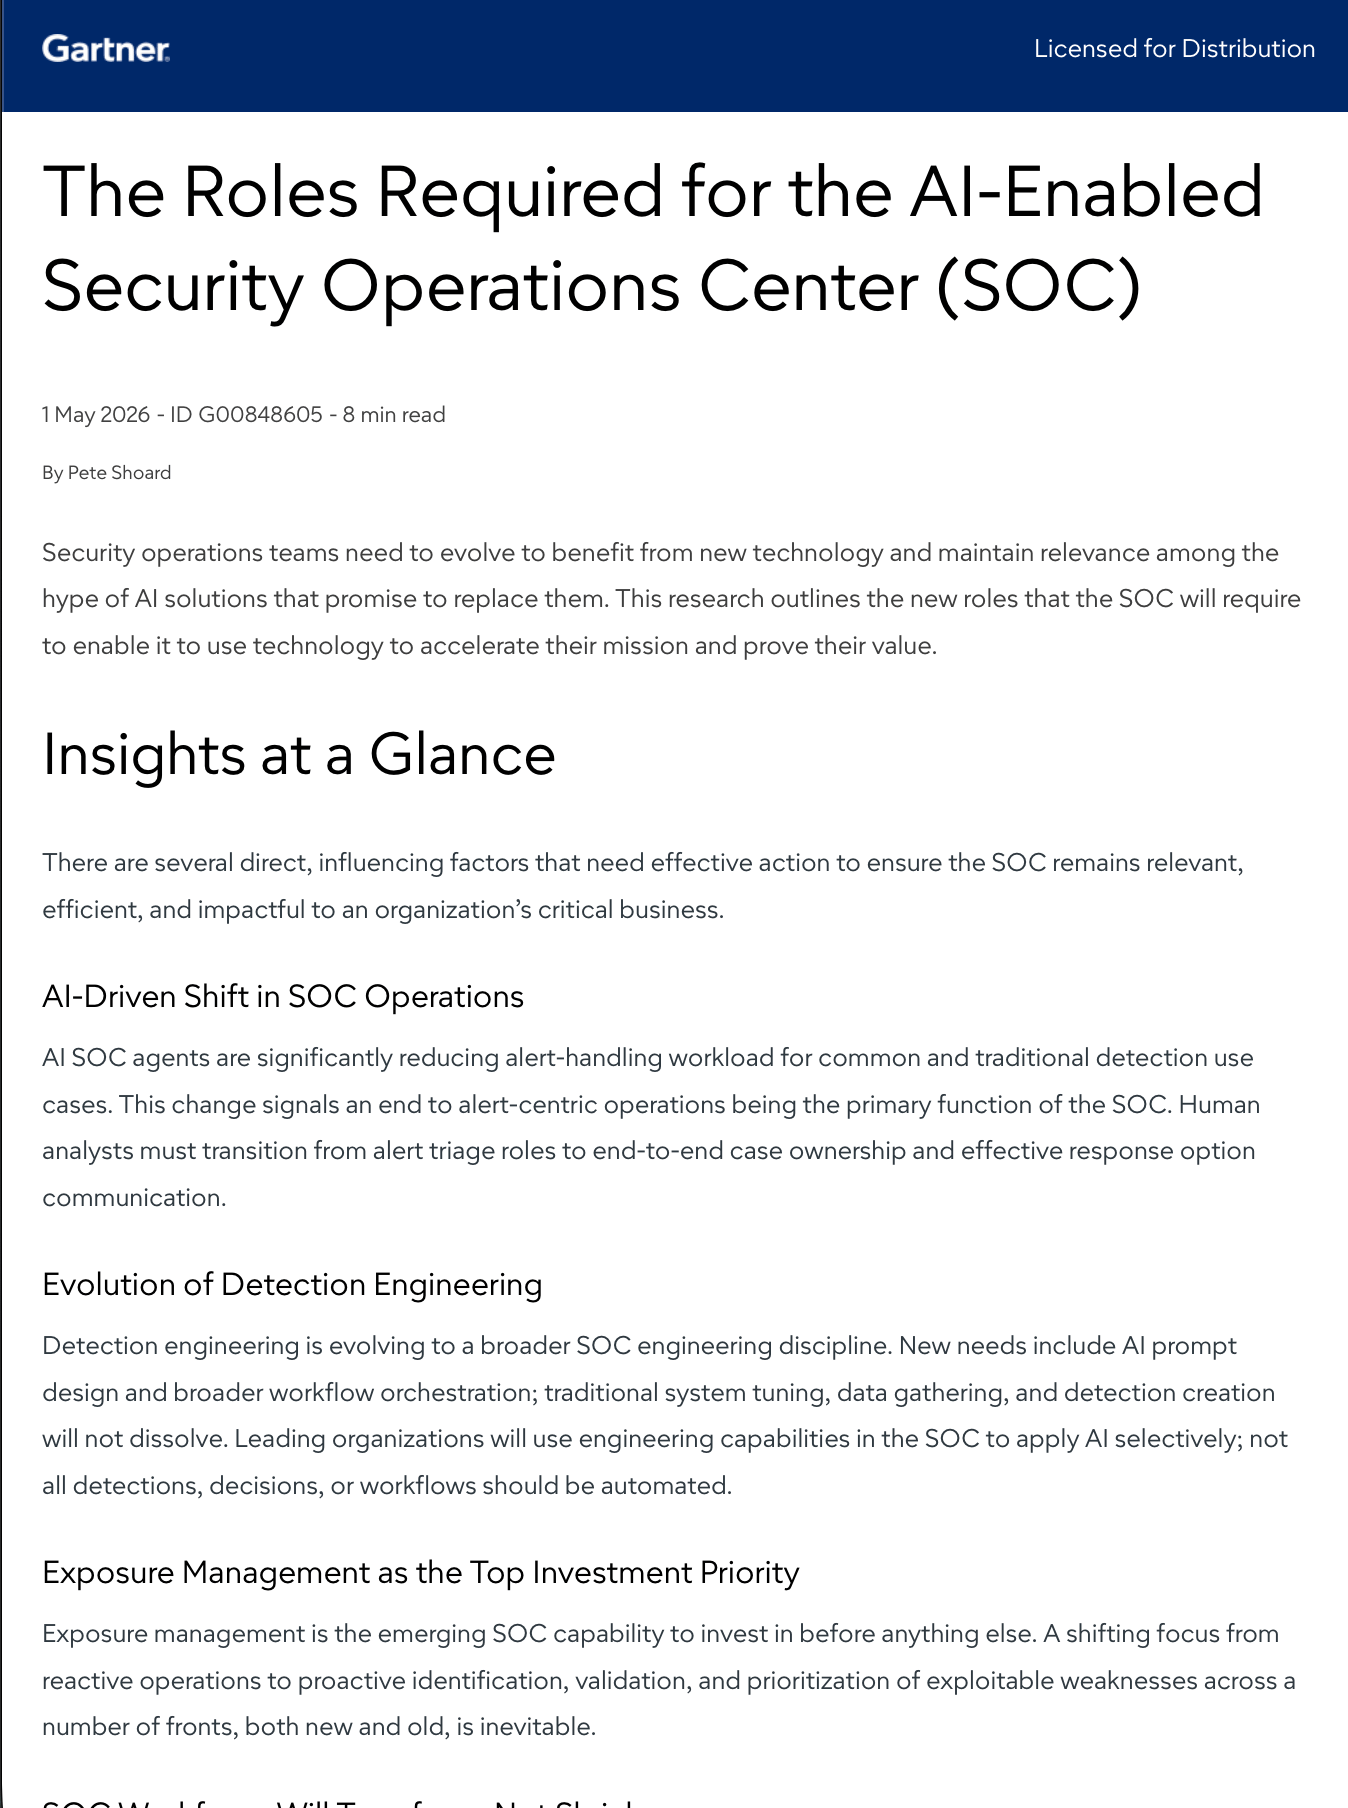
The Roles Your AI-Enabled SOC Will Need
Gartner research on how SOC roles shift as AI SOC agents reduce alert-handling work

Jon is the Head of Security Operations at Prophet Security where he is focused on building the next wave of SOC innovation by leveraging AI to automate the manual, repetitive tasks of alert triage and investigation. Previously, he was the VP of Security Operations at Rapid7 and Expel.